
[Feb 08, 2024] Pass Your 300-730 Dumps Free Latest Cisco Practice Tests
Get Top-Rated Cisco 300-730 Exam Dumps Now
Cisco 300-730 certification exam is designed for professionals who want to validate their knowledge and skills in implementing secure solutions with virtual private networks (VPNs). Implementing Secure Solutions with Virtual Private Networks certification exam is a part of the Cisco Certified Network Professional (CCNP) Security certification track and focuses on the implementation, troubleshooting, and monitoring of VPNs. 300-730 exam covers various topics such as secure communication, VPN technologies, and VPN routing and forwarding.
What skills and knowledge are required for Cisco 300-730 Exam?
Cisco 300-730 Exam is an important exam, especially for those who want to work in the Information Technology industry. If you wish to have a high-paying job in this competitive industry, it is important that you pass this test. BraindumpsPass gave me the confidence I needed to pass and I am so glad I purchased their study guide. This program was extremely helpful and easy to use. They provided everything I needed inside of it, including practice exams and testing questions. I felt prepared for the real test and didn't have any surprises during the actual test. BraindumpsPass made my studying easy and enjoyable. I would highly recommend this program to anyone who wants to pass this exam on the first try with 300-730 Dumps. From Jessica Ellington, I have been out of school for a while now, but when I decided to go back to school for computer networking certification, I was worried about if I was going to be able to get through the course with my class schedule (which is pretty full). The only way that was going to happen was if I had a little extra help getting through the material quickly enough. BraindumpsPass came with all of the assistance that I needed, so I knew that I would be able to do well on the exam by using their study material.
NEW QUESTION # 66
Refer to the exhibit.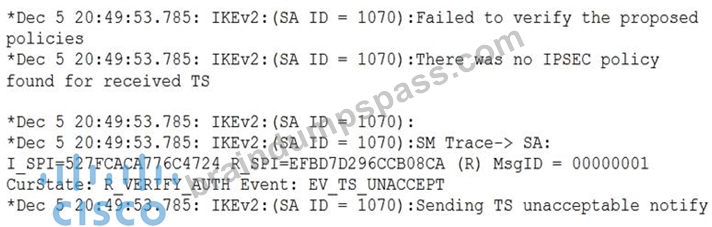
An IKEv2 site-to-site tunnel between an ASA and a remote peer is not building successfully. What will fix the problem based on the debug output?
- A. Specify the peer IP address in the tunnel group name.
- B. Correct crypto access list on both VPN devices.
- C. Install the correct certificate to validate the peer.
- D. Ensure crypto IPsec policy matches on both VPN devices.
Answer: B
Explanation:
To fix the problem with the IKEv2 site-to-site tunnel between an ASA and a remote peer based on the debug output, you should ensure that the crypto IPsec policy matches on both VPN devices. The debug output indicates that the crypto policies on the two VPN devices are mismatched, which is preventing the tunnel from building successfully. Installing the correct certificate to validate the peer, correcting the crypto access list on both VPN devices, and specifying the peer IP address in the tunnel group name will not fix the problem.
NEW QUESTION # 67
A network engineer must implement an SSLVPN Cisco AnyConnect solution that supports 500 concurrent users, ensures all traffic from the client passes through the ASA, and allows users to access all devices on the inside interface subnet (192.168.0.0/24). Assuming all other configuration is set up appropriately, which configuration implements this solution?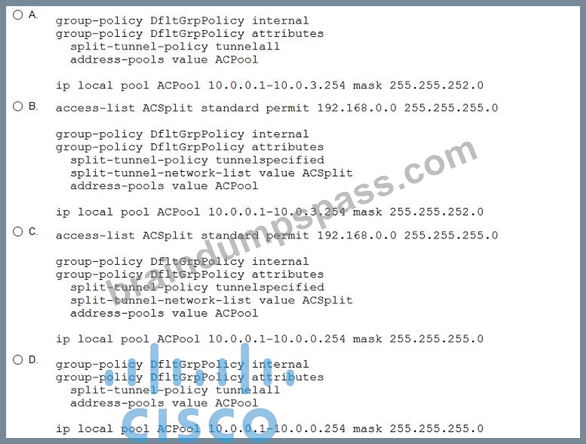
- A. Option A
- B. Option B
- C. Option C
- D. Option D
Answer: A
Explanation:
"ensures all traffic from the client passes through the ASA" that is one of the requirements. Meaning all traffic should pass through the tunnel, I know they mention 192.168.0.0 network but that is just to confuse.
NEW QUESTION # 68
What is a requirement for smart tunnels to function properly?
- A. Applications must be UDP.
- B. Java or ActiveX must be enabled on the client machine.
- C. The user on the client machine must have admin access.
- D. Stateful failover must not be configured.
Answer: B
NEW QUESTION # 69
Refer to the exhibit.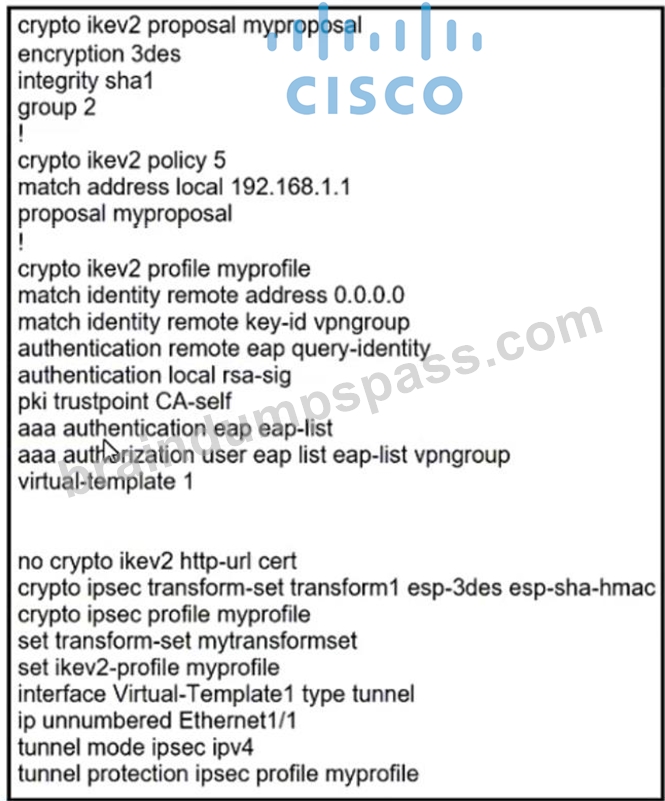
Based on the output of the show run command, which remote access VPN technology is configured?
- A. PPTP
- B. SSLVPN Full Tunnel
- C. clientless SSLVPN
- D. FlexVPN
Answer: D
NEW QUESTION # 70
What is a characteristic of GETVPN?
- A. Quick mode is used to create an IPsec SA.
- B. The remote peer for the IPsec session is configured as part of the crypto map.
- C. An ACL that defines interesting traffic must be configured and applied to the crypto map.
- D. All peers have one IPsec SPI for inbound and outbound communication.
Answer: D
Explanation:
In GETVPN, all group members share a common security association (SA) database and the same keys for encryption and decryption. This approach avoids the need for per-peer IPsec SAs and simplifies the configuration and management of the VPN. Instead of using multiple SAs, GETVPN uses a single SA with a unique Group Domain of Interpretation (GDOI) group key that is distributed to all group members.
NEW QUESTION # 71 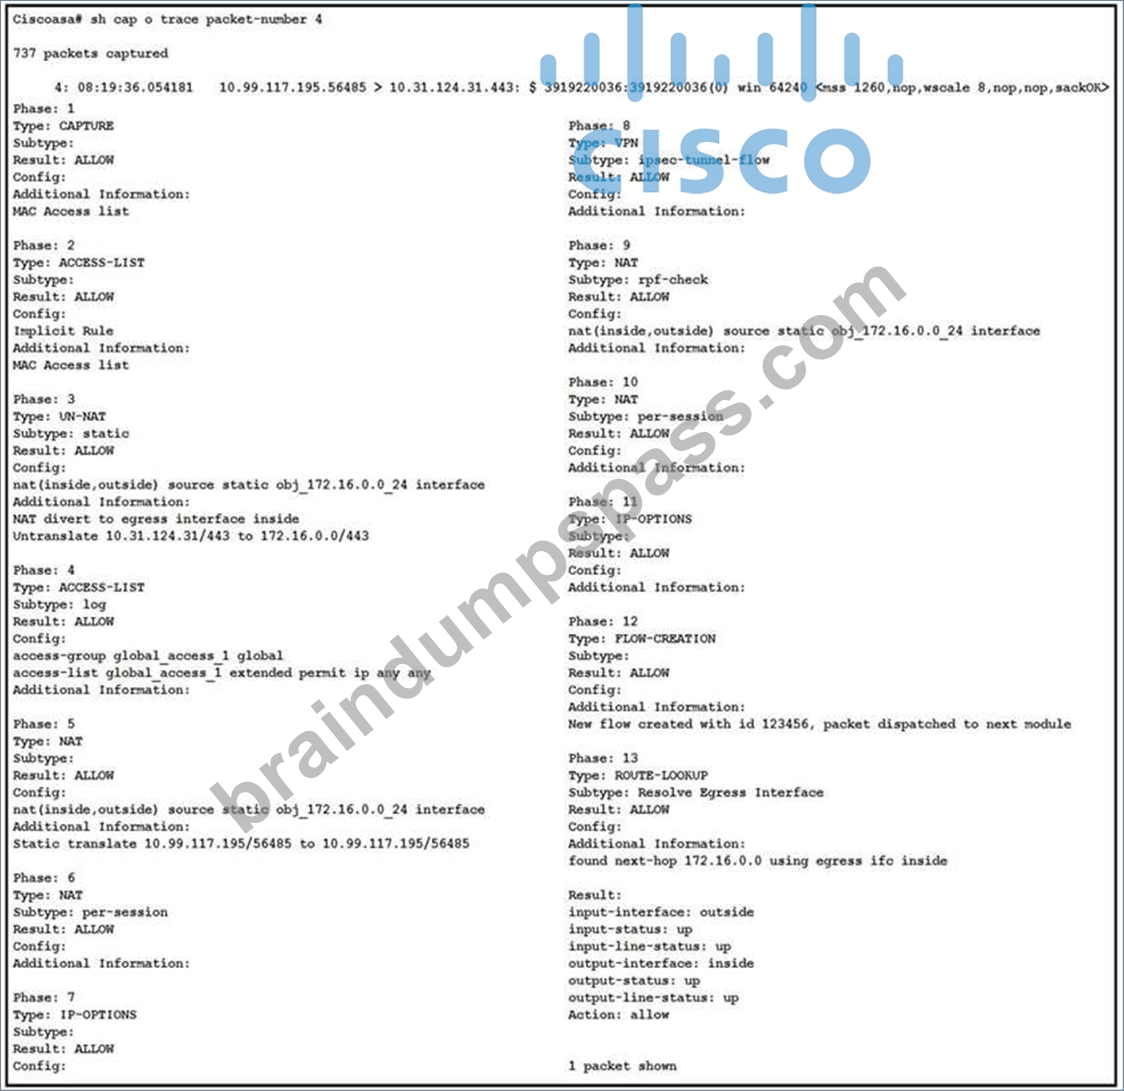
Refer to the exhibit. An SSL client is connecting to an ASA headend. The session fails with the message
"Connection attempt has timed out. Please verify Internet connectivity." Based on how the packet is processed, which phase is causing the failure?
- A. phase 3: UN-NAT
- B. phase 4: ACCESS-LIST
- C. phase 9: rpf-check
- D. phase 5: NAT
Answer: A
Explanation:
Section: Troubleshooting using ASDM and CLI
NEW QUESTION # 72
Which two types of SSO functionality are available on the Cisco ASA without any external SSO servers? (Choose two.)
- A. NTLM
- B. Kerberos
- C. OAuth 2.0
- D. SAML
- E. HTTP Basic
Answer: A,E
Explanation:
The auto-signon command is a single sign-on method for users of clientless SSL VPN sessions. It passes the login credentials (username and password) to internal servers for authentication using NTLM authentication, basic authentication, or both. Multiple auto-signon commands can be entered and are processed according to the input order (early commands take precedence).
https://www.cisco.com/c/en/us/td/docs/security/asa/asa916/configuration/vpn/asa-916-vpn-config/webvpn-configure-policy-groups.html#ID-2439-00001438
NEW QUESTION # 73
Which two features provide headend resiliency for Cisco AnyConnect clients? (Choose two.)
- A. ASA failover
- B. AnyConnect Auto Reconnect
- C. AnyConnect Network Access Manager
- D. AnyConnect Backup Servers
- E. AnyConnect Always On
Answer: A,D
Explanation:
According to the Implementing Secure Solutions with Virtual Private Networks (SVPN) documents and learning resources available at cisco.com, the two features that provide headend resiliency for Cisco AnyConnect clients are:
AnyConnect Backup Servers: This feature allows the AnyConnect client to automatically connect to a backup server in case the primary server is unreachable or fails. The backup server list is configured on the ASA or IOS headend and pushed to the client during the VPN connection establishment. The client can also manually select a backup server from the list if needed. This feature enhances the availability and reliability of the VPN service for the clients12.
ASA failover: This feature enables two identical ASAs to be paired together as an active/standby or active/active pair. The ASAs synchronize their configuration and state information and monitor each other's health. If the active ASA fails or becomes unreachable, the standby ASA takes over the traffic and VPN sessions without any disruption for the clients. This feature provides high availability and redundancy for the VPN headend34.
1: AnyConnect Backup Servers 2: Redundancy options for IOS Headend for AnyConnect Clients 3: ASA Failover 4: AnyConnect Implementation and Performance/Scaling Reference for COVID-19 Preparation
NEW QUESTION # 74
A network engineer must implement an SSLVPN Cisco AnyConnect solution that supports 500 concurrent users, ensures all traffic from the client passes through the ASA, and allows users to access all devices on the inside interface subnet (192.168.0.0/24). Assuming all other configuration is set up appropriately, which configuration implements this solution?
- A. Option A
- B. Option B
- C. Option C
- D. Option D
Answer: A
NEW QUESTION # 75
Refer to the exhibit.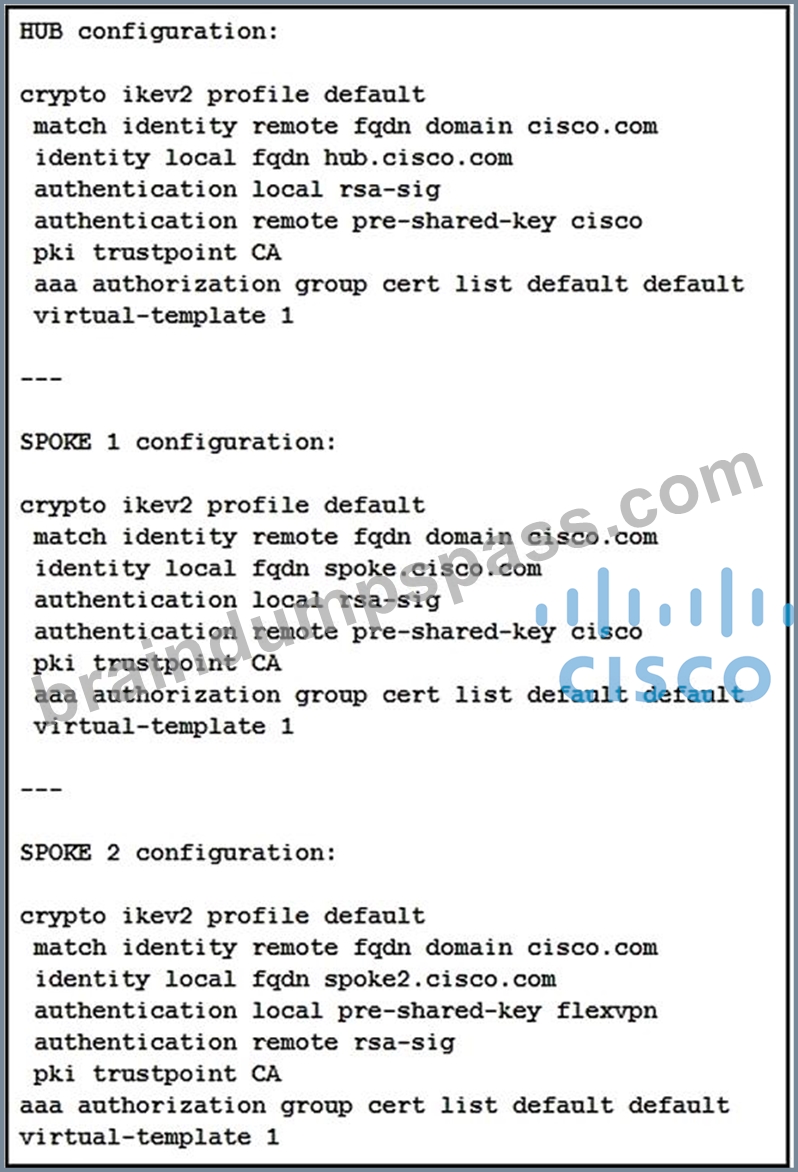
What is a result of this configuration?
- A. Spoke 2 fails the authentication because the remote authentication method is incorrect.
- B. Spoke 1 passes the authentication to the hub and successfully proceeds to phase 2.
- C. Spoke 2 passes the authentication to the hub and successfully proceeds to phase 2.
- D. Spoke 1 fails the authentication because the authentication methods are incorrect.
Answer: D
NEW QUESTION # 76
Which two features provide headend resiliency for Cisco AnyConnect clients? (Choose two.)
- A. AnyConnect Auto Reconnect
- B. AnyConnect Network Access Manager
- C. AnyConnect Always On
- D. AnyConnect Backup Servers
- E. ASA failover
Answer: A,C
Explanation:
The two features that provide headend resiliency for Cisco AnyConnect clients are AnyConnect Auto Reconnect and AnyConnect Always On. AnyConnect Auto Reconnect allows the client to attempt to automatically reconnect to the same or a different headend in the event of a session disruption. AnyConnect Always On allows the client to remain connected to the headend at all times, even if the client is idle or the connection is interrupted. Additionally, AnyConnect Backup Servers allow the client to connect to a backup headend if the primary headend is unreachable, and ASA failover provides an additional layer of redundancy for the headend itself.
NEW QUESTION # 77
Which two protocols does DMVPN leverage to build dynamic VPNs to multiple destinations? (Choose two.)
- A. GDOI
- B. IKEv2
- C. mBGP
- D. mGRE
- E. NHRP
Answer: D,E
NEW QUESTION # 78
Which method dynamically installs the network routes for remote tunnel endpoints?
- A. policy-based routing
- B. reverse route injection
- C. route filtering
- D. CEF
Answer: B
Explanation:
Reference:
<https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/sec_conn_vpnav/configuration/12-4t/sec-vpn- availability-12-4t-book/sec-rev-rte-inject.html>
NEW QUESTION # 79
Which command shows the smart default configuration for an IPsec profile?
- A. show run all crypto ipsec profile
- B. ipsec profile does not have any smart default configuration
- C. show smart-defaults ipsec profile
- D. show crypto ipsec profile default
Answer: D
Explanation:
The following table lists the commands that are enabled with the IKEv2 Smart Defaults feature, along with the default values.
...
Device# show crypto ipsec profile default
IPSEC profile default
Security association lifetime: 4608000 kilobytes/3600 seconds
Responder-Only (Y/N): N
PFS (Y/N): N
Transform sets={
default: { esp-aes esp-sha-hmac },
}
https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/sec_conn_ike2vpn/configuration/xe-3s/sec-flex-vpn-xe-3s-book/sec-cfg-ikev2-flex.html
NEW QUESTION # 80
Users are getting untrusted server warnings when they connect to the URL https://asa.lab from their browsers. This URL resolves to 192.168.10.10, which is the IP address for a Cisco ASA configured for a clientless VPN. The VPN was recently set up and issued a certificate from an internal CA server. Users can connect to the VPN by ignoring the message, however, when users access other webservers that use certificates issued by the same internal CA server, they do not experience this issue. Which action resolves this issue?
- A. Import the CA that signed the certificate into the user trusted root CA store.
- B. Import the CA that signed the certificate into the machine trusted root CA store.
- C. Reissue the certificate with asa.lab in the subject alternative name field.
- D. Reissue the certificate with 192.168.10.10 in the subject common name field.
Answer: C
Explanation:
https://www.cisco.com/c/en/us/support/docs/security-vpn/public-key-infrastructure-pki/200339-Configure-ASA-SSL-Digital-Certificate-I.html
NEW QUESTION # 81
Refer to the exhibit.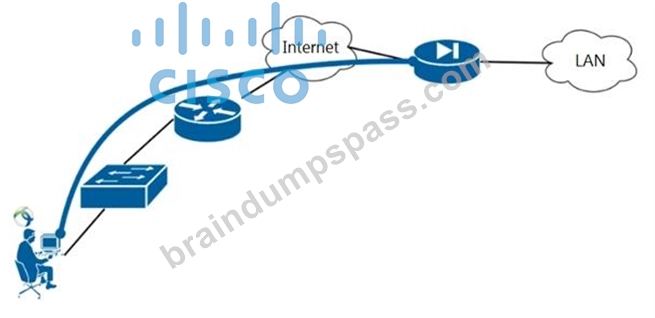
A user is connecting from behind a PC with a private IP Address. Their ISP provider is blocking TCP port 443. Which AnyConnect XML configuration will allow the user to establish a connection with the ASA?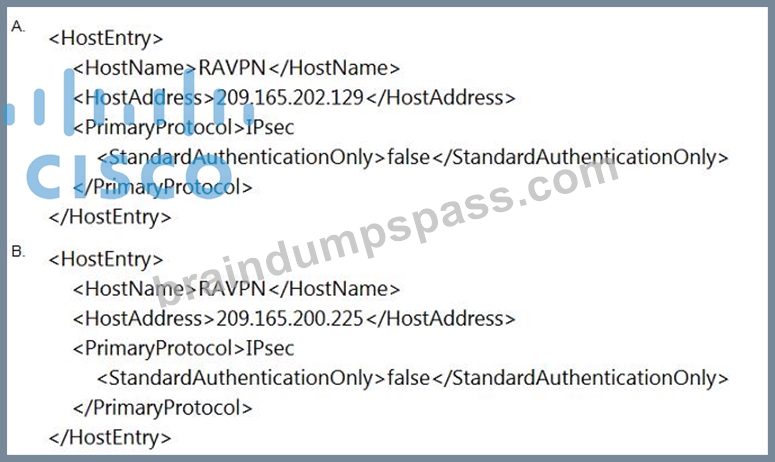
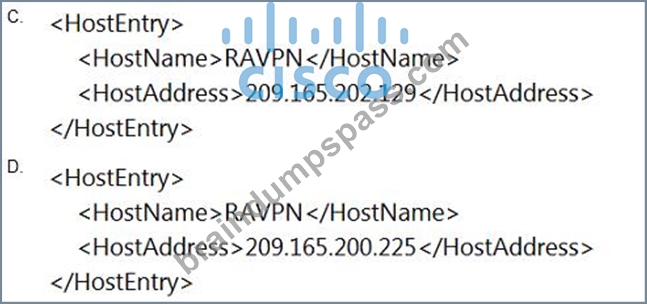
- A. Option D
- B. Option A
- C. Option B
- D. Option C
Answer: A
NEW QUESTION # 82
A network engineer has almost finished setting up a clientless VPN that allows remote users to access internal HTTP servers. Users must enter their username and password twice: once on the clientless VPN web portal and again to log in to internal HTTP servers. The Cisco ASA and the HTTP servers use the same Active Directory server to authenticate users. Which next step must be taken to allow users to enter their password only once?
- A. Set up the Cisco ASA to authenticate users via a SAML 2.0 IDP.
- B. Configure auto-sign-on using NTLM authentication.
- C. Use LDAPS and add password management to the clientless tunnel group.
- D. Create smart tunnels for the HTTP servers.
Answer: B
NEW QUESTION # 83
Refer to the exhibit.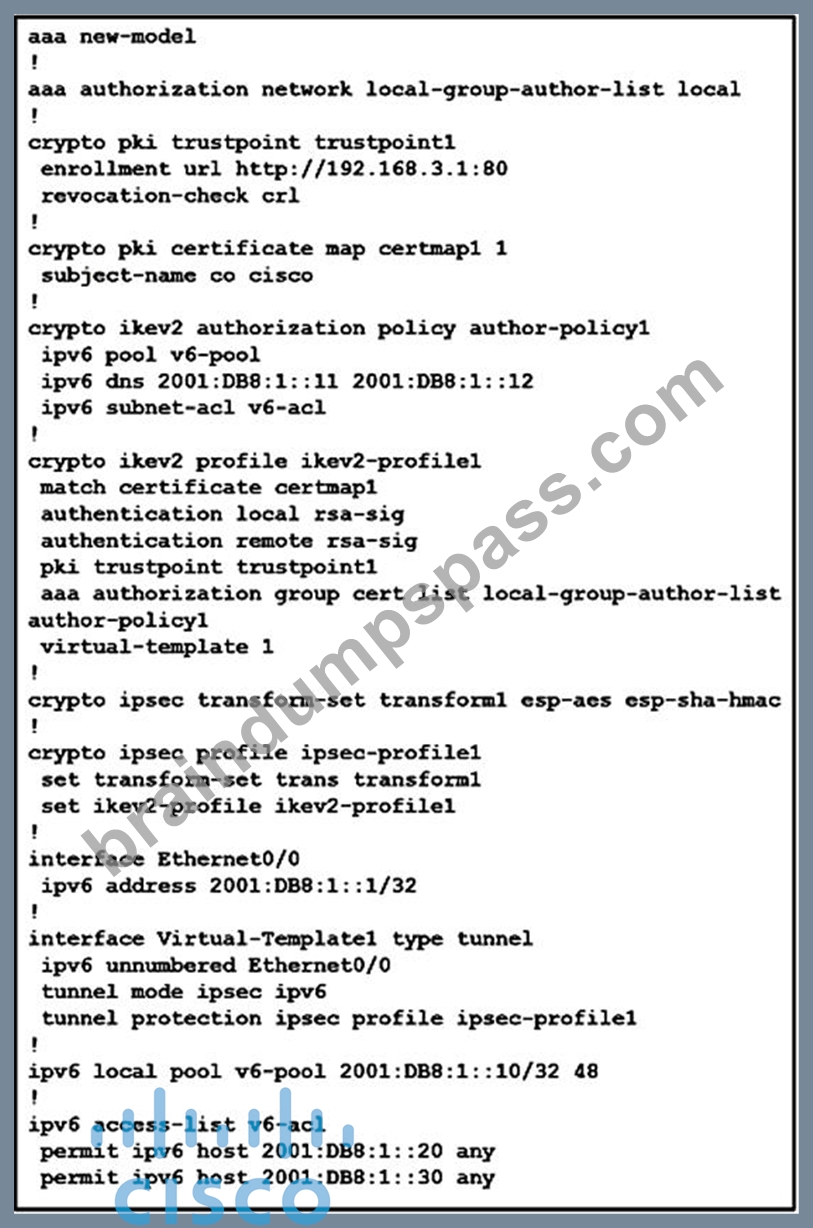
What is configured as a result of this command set?
- A. FlexVPN server to authenticate IPv6 peers by using EAP
- B. FlexVPN client profile for IPv6
- C. FlexVPN server for an IPv6 dVTI session
- D. FlexVPN server to authorize groups by using an IPv6 external AAA
Answer: B
NEW QUESTION # 84
Under which section must a bookmark or URL list be configured on a Cisco ASA to be available for clientless SSLVPN users?
- A. tunnel-group (general-attributes)
- B. webvpn (group-policy)
- C. tunnel-group (webvpn-attributes)
- D. webvpn (global configuration)
Answer: B
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/asa/asa97/configuration/vpn/asa-97-vpn-config/webvpn-configure-policy-groups.html says clearly: In group-policy webvpn configuration mode, you can specify (list of things, including url-list).
NEW QUESTION # 85
Refer to the exhibit.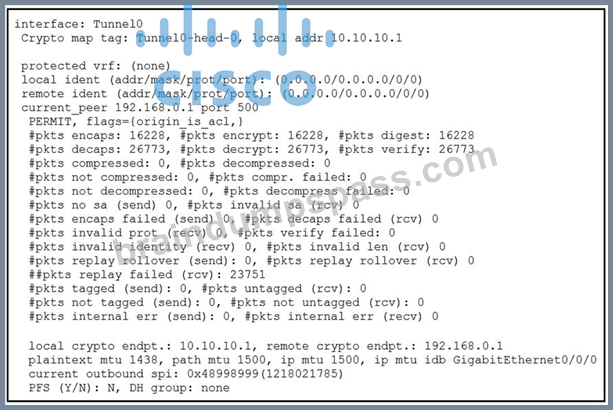
Upon setting up a tunnel between two sites, users are complaining that connections to applications over the VPN are not working consistently. The output of show crypto ipsec sa was collected on one of the VPN devices. Based on this output, what should be done to fix this issue?
- A. Make an adjustment to IPSec replay window.
- B. Enable perfect forward secrecy.
- C. Lower the tunnel MTU.
- D. Specify the application networks in the remote identity.
Answer: A
Explanation:
https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/sec_conn_dplane/configuration/xe-16-8/sec-ipsec-data-plane-xe-16-8-book/sec-ipsec-antireplay.html#GUID-1FF00FBB-0746-48B2-A02A-2BB066BEDEF8
NEW QUESTION # 86
Which clientless SSLVPN supported feature works when the http-only-cookie command is enabled?
- A. Java rewriter -
- B. Java plug-ins
- C. script browser
- D. port reflector
- E. Citrix load balancer
Answer: B
Explanation:
https://www.cisco.com/c/en/us/td/docs/security/asa/asa94/config-guides/asdm74/vpn/asdm-74-vpn-config/webvpn-troubleshooting.html The following Clientless SSL VPN features will not work when the http-only-cookie command is enabled:
* Java plug-ins
* Java rewriter
* Port forwarding
* File browser
* Sharepoint features that require desktop applications (for example, MS Office applications)
* AnyConnect Web launch
* Citrix Receiver, XenDesktop, and Xenon
* Other non-browser-based and browser plugin-based applications
NEW QUESTION # 87
After a user configures a connection profile with a bookmark list and tests the clientless SSLVPN connection, all of the bookmarks are grayed out. What must be done to correct this behavior?
- A. Configure a DNS server on the Cisco ASA and verify it has a record for the web server.
- B. Specify the correct port for the web server under the bookmark.
- C. Verify HTTP/HTTPS connectivity between the Cisco ASA and the web server.
- D. Apply the bookmark to the correct group policy.
Answer: A
NEW QUESTION # 88
......
Passing Key To Getting 300-730 Certified Exam Engine PDF: https://www.braindumpspass.com/Cisco/300-730-practice-exam-dumps.html
300-730 Exam Dumps Pass with Updated Tests Dumps: https://drive.google.com/open?id=1TeuP-SHdALhIGShsnCSrKUSe822wowSL