
Steps Necessary To Pass The PCNSA Exam from Training Expert BraindumpsPass
Valid Way To Pass Paloalto Network Security Administrator's PCNSA Exam
NEW QUESTION # 137
An administrator needs to allow users to use only certain email applications.
How should the administrator configure the firewall to restrict users to specific email applications?
- A. Create an application group and add the email applications to it.
- B. Create an application filter and filter it on the collaboration category, email subcategory.
- C. Create an application filter and filter it on the collaboration category.
- D. Create an application group and add the email category to it.
Answer: A
NEW QUESTION # 138
Which three configuration settings are required on a Palo Alto networks firewall management interface?
- A. netmask
- B. hostname
- C. default gateway
- D. IP address
- E. auto-negotiation
Answer: A,C,D
NEW QUESTION # 139
Which stage of the cyber-attack lifecycle makes it important to provide ongoing education to users on spear phishing links, unknown emails, and risky websites?
- A. exploitation
- B. installation
- C. reconnaissance
- D. delivery
Answer: D
Explanation:
Weaponization and Delivery: Attackers will then determine which methods to use in order to deliver malicious payloads. Some of the methods they might utilize are automated tools, such as exploit kits, spear phishing attacks with malicious links, or attachments and malvertizing. Gain full visibility into all traffic, including SSL, and block high-risk applications. Extend those protections to remote and mobile devices.
Protect against perimeter breaches by blocking malicious or risky websites through URL filtering. Block known exploits, malware and inbound command-and- control communications using multiple threat prevention disciplines, including IPS, anti-malware, anti-CnC, DNS monitoring and sinkholing, and file and content blocking.
Detect unknown malware and automatically deliver protections globally to thwart new attacks. Provide ongoing education to users on spear phishing links, unknown emails, risky websites, etc.
https://www.paloaltonetworks.com/cyberpedia/how-to-break-the-cyber-attack-lifecycle
NEW QUESTION # 140
Which plane on a Palo alto networks firewall provides configuration logging and reporting functions on a separate processor?
- A. management
- B. data
- C. network processing
- D. security processing
Answer: A
NEW QUESTION # 141
Which two configuration settings shown are not the default? (Choose two.)
- A. Enable Security Log
- B. Server Log Monitor Frequency (sec)
- C. Enable Probing
- D. Enable Session
Answer: B,D
Explanation:
Explanation/Reference: https://docs.paloaltonetworks.com/pan-os/8-0/pan-os-web-interface-help/user-identification/device- user-identification-user-mapping/enable-server-monitoring
NEW QUESTION # 142
Match the Palo Alto Networks Security Operating Platform architecture to its description.
Answer:
Explanation: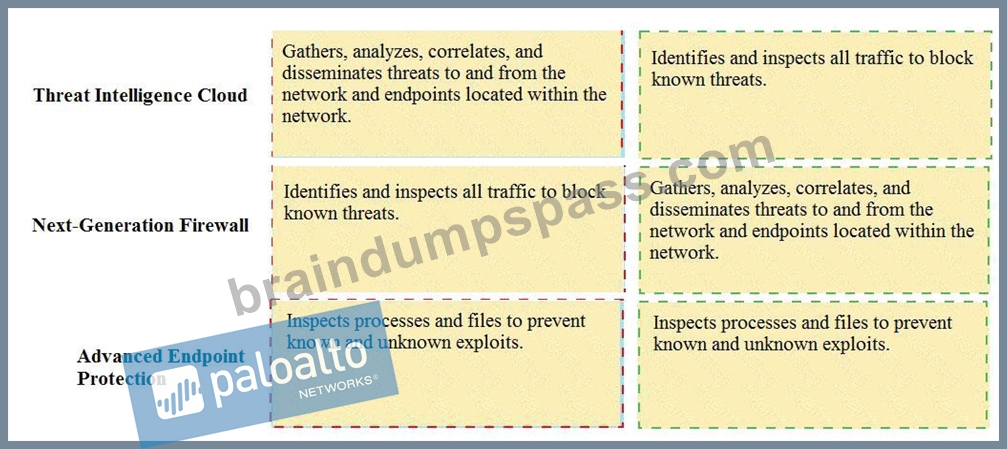
Explanation
Threat Intelligence Cloud - Gathers, analyzes, correlates, and disseminates threats to and from the network and endpoints located within the network.
Next-Generation Firewall - Identifies and inspects all traffic to block known threats Advanced Endpoint Protection - Inspects processes and files to prevent known and unknown exploits
NEW QUESTION # 143
Order the steps needed to create a new security zone with a Palo Alto Networks firewall.
Answer:
Explanation:
Explanation
Step 1 - Select network tab
Step 2 - Select zones from the list of available items
Step 3 - Select Add
Step 4 - Specify Zone Name
Step 5 - Specify Zone Type
Step 6 - Assign interfaces as needed
NEW QUESTION # 144
An administrator receives a global notification for a new malware that infects hosts. The infection will result in the infected host attempting to contact a command-and-control (C2) server. Which two security profile components will detect and prevent this threat after the firewall's signature database has been updated?
(Choose two.)
- A. vulnerability protection profile applied to outbound security policies
- B. URL filtering profile applied to outbound security policies
- C. anti-spyware profile applied to outbound security policies
- D. antivirus profile applied to outbound security policies
Answer: B,C
NEW QUESTION # 145
Arrange the correct order that the URL classifications are processed within the system.
Answer:
Explanation:
Explanation
First - Block List
Second - Allow List
Third - Custom URL Categories
Fourth - External Dynamic Lists
Fifth - Downloaded PAN-DB Files
Sixth - PAN-DB Cloud
NEW QUESTION # 146
Match the network device with the correct User-ID technology.
Answer:
Explanation:
NEW QUESTION # 147
Given the topology, which zone type should zone A and zone B to be configured with?
- A. Layer2
- B. Layer3
- C. Tap
- D. Virtual Wire
Answer: B
NEW QUESTION # 148
Which Palo Alto Networks service protects cloud-based applications such as Dropbox and Salesforce by monitoring permissions and shares and scanning files for sensitive information?
- A. Prisma SaaS
- B. Panorama
- C. GlobalProtect
- D. AutoFocus
Answer: A
NEW QUESTION # 149
Which type of profile must be applied to the Security policy rule to protect against buffer overflows illegal code execution and other attempts to exploit system flaws''
- A. URL filtering
- B. file blocking
- C. anti-spyware
- D. vulnerability protection
Answer: D
NEW QUESTION # 150
Which statement is true about Panorama managed devices?
- A. Local configuration locks can be manually unlocked from Panorama
- B. Local configuration locks prohibit Security policy changes for a Panorama managed device
- C. Security policy rules configured on local firewalls always take precedence
- D. Panorama automatically removes local configuration locks after a commit from Panorama
Answer: C
Explanation:
Explanation
Explanation/Reference:
Reference:
<https://docs.paloaltonetworks.com/panorama/9-1/panorama-admin/administer-panorama/manage- locks-forrestricting-configuration-changes.html>
NEW QUESTION # 151
Which administrator type provides more granular options to determine what the administrator can view and modify when creating an administrator account?
- A. Root
- B. Dynamic
- C. Superuser
- D. Role-based
Answer: B
Explanation:
https://docs.paloaltonetworks.com/pan-os/9-0/pan-os-admin/firewall-administration/manage-firewall-administrators/administrative-role-types#id8b324bf1-eac8-
40e1-82d5-6f82ff761fa9
NEW QUESTION # 152
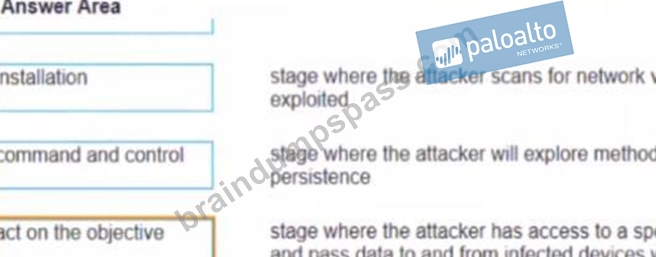
Match the cyber-attack lifecycle stage to its correct description.
Answer:
Explanation:
NEW QUESTION # 153
Match the Cyber-Attack Lifecycle stage to its correct description.
Answer:
Explanation:
Explanation
Reconnaissance - stage where the attacker scans for network vulnerabilities and services that can be exploited.
Installation - stage where the attacker will explore methods such as a root kit to establish persistence Command and Control - stage where the attacker has access to a specific server so they can communicate and pass data to and from infected devices within a network.
Act on the Objective - stage where an attacker has motivation for attacking a network to deface web property
NEW QUESTION # 154 
Given the topology, which zone type should interface E1/1 be configured with?
- A. Layer3
- B. Tap
- C. Virtual Wire
- D. Tunnel
Answer: B
NEW QUESTION # 155
Match the network device with the correct User-ID technology.
Answer:
Explanation:
NEW QUESTION # 156
Which feature would be useful for preventing traffic from hosting providers that place few restrictions on content, whose services are frequently used by attackers to distribute illegal or unethical material?
- A. Palo Alto Networks Known Malicious IP Addresses
- B. Palo Alto Networks C&C IP Addresses
- C. Palo Alto Networks Bulletproof IP Addresses
- D. Palo Alto Networks High-Risk IP Addresses
Answer: C
Explanation:
To block hosts that use bulletproof hosts to provide malicious, illegal, and/or unethical content, use the bulletproof IP address list in policy.
NEW QUESTION # 157
Based on the security policy rules shown, ssh will be allowed on which port?
- A. any port
- B. same port as ssl and snmpv3
- C. the default port
- D. only ephemeral ports
Answer: C
NEW QUESTION # 158
Which the app-ID application will you need to allow in your security policy to use facebook-chat?
- A. facebook-base
- B. facebook
- C. facebook-chat
- D. facebook-email
Answer: A,C
NEW QUESTION # 159
......
All PCNSA Dumps and Palo Alto Networks Certified Network Security Administrator Training Courses: https://www.braindumpspass.com/Palo-Alto-Networks/PCNSA-practice-exam-dumps.html
Free Test Engine For Palo Alto Networks Certified Network Security Administrator Certification Exams: https://drive.google.com/open?id=1sGN3pxXQPZPZtcXrZo5Ui2F08DGaf4nl