
Pass PCCSE Exam in First Attempt Guaranteed 100% Cover Real Exam Questions [Aug-2022]
Valid PCCSE test answers & Palo Alto Networks PCCSE exam pdf
The benefit in Obtaining the Palo-Alto-Networks PCCSE: Prisma Certified Cloud Security Engineer Exam Certification
Through completing their courses and having access to revision resources for seven months after the end, candidates would have a more comprehensive know-how than an uncertified expert when it comes to different technology and programs. In this specific skill range, certified professionals are 74 percent more able to perform their assignments on schedule.
Being a Palo Alto Network Certified Network Security Engineer ensures the one item that the organisation values and therefore a better compensation plan is worth to you. On average, a member of a qualified Palo Alto Networks Network Security Engineer team is calculated to be 30% higher than its uncertified technical members.
After the Palo Alto Network Accredited Security Engineer Certification applicants have completed their programs, they have received a Palo Alto official assurance that they have already received the certification in their area. You will also apply this to your CV, cover letters and work requests.
In terms of their preparation, organizational owners invest a lot in their workers in order to increase speed, efficiency and understanding of their importance to them. Certified professionals can limit the amount he spends on projects, which means that he will do more to minimize business failure if device glitches are repaired or hardware difficulties resolved.
If you qualify to be employed or seeking to become a promoter at your present location, you will be listed as top candidates by the Palo Alto Network Certified Network Security Engineer qualification in the area in which you applicate.
Palo Alto PCCSE Exam Certification Details:
| Exam Registration | PEARSON VUE |
| Duration | 90 minutes |
| Passing Score | Variable (70-80 / 100 Approx.) |
| Number of Questions | 75-85 |
| Recommended Training | Prisma Cloud - Monitoring and Securing (EDU-150) Prisma Cloud - Onboarding and Operationalizing (EDU-152) |
| Exam Code | PCCSE |
| Exam Name | Cloud Security Engineer |
| Sample Questions | Palo Alto PCCSE Sample Questions |
Palo-Alto-Networks PCCSE: Prisma Certified Cloud Security Engineer Exam topics
Candidates must know the exam topics before they start of preparation. Because it will really help them in hitting the core. Our PCCSE exam dumps pdf will include the following topics:
- Deploying and Configure 23%
- Core Concepts 23%
- Planning 16%
- Configuration Troubleshooting 18%
- Operation 20%
Along with that, the following are some important aspects of the exam and covered in PCCSE exam dumps.
- User-ID
- Security Platform and Architecture
- Interface Configuration
- URL Filtering
- Next Generation Security Practices
- GlobalProtect
- WildFire
- Security and NAT Policies
- Decryption
NEW QUESTION 47
You have onboarded a public cloud account into Prisma Cloud Enterprise Configuration Resource ingestion is visible in the Asset Inventory for the onboarded account, but no alerts are being generated for the configuration assets in the account Config policies are enabled in the Prisma Cloud Enterprise tenant, with those policies associated to existing alert rules RQL statements on the Investigate matching those policies return config resource results successfully Why are no alerts being generated''
- A. The public cloud account does not have access to configuration resources.
- B. The public cloud account is not associated with an alert rule
- C. The public cloud account does not have audit trail ingestion enabled.
- D. The public cloud account is not associated with an alert notification.
Answer: D
NEW QUESTION 48
The administrator wants to review the Console audit logs from within the Console.
Which page in the Console should the administrator use to review this data, if it can be reviewed at all?
- A. Navigate to Manage > Defenders > View Logs
- B. Navigate to Manage > View Logs > History
- C. The audit logs can be viewed only externally to the Console
- D. Navigate to Monitor > Events > Host Log Inspection
Answer: B
NEW QUESTION 49
A Prisma Cloud administrator is onboarding a single GCP project to Prisma Cloud. Which two steps can be performed by the Terraform script? (Choose two.)
- A. create the Prisma Cloud role.
- B. enable flow logs for Prisma Cloud.
- C. publish the flow log to a storage bucket.
- D. enable the required APIs for Prisma Cloud.
Answer: B,D
NEW QUESTION 50
Which three options are selectable in a CI policy for image scanning with Jenkins or twistcli? (Choose three.)
- A. Scope - Scans run on a particular host
- B. Failure threshold
- C. Grace Period
- D. Apply rule only when vendor fixes are available
- E. Credential
Answer: B,C,E
NEW QUESTION 51
An administrator sees that a runtime audit has been generated for a container.
The audit message is:
"/bin/ls launched and is explicitly blocked in the runtime rule. Full command: ls -latr" Which protection in the runtime rule would cause this audit?
- A. Container
- B. Networking
- C. Processes
- D. File systems
Answer: A
NEW QUESTION 52
Which three types of buckets exposure are available in the Data Security module? (Choose three.)
- A. International
- B. Public
- C. Differential
- D. Private
- E. Conditional
Answer: A,C,E
NEW QUESTION 53
The development team wants to fail CI jobs where a specific CVE is contained within the image. How should the development team configure the pipeline or policy to produce this outcome?
- A. Set the specific CVE exception as an option in Jenkins or twistcli.
- B. Set the specific CVE exception as an option using the magic string in the Console.
- C. Set the specific CVE exception as an option in Defender running the scan.
- D. Set the specific CVE exception in Console's CI policy.
Answer: D
Explanation:
Explanation
Reference tech docs:
https://docs.paloaltonetworks.com/prisma/prisma-cloud/prisma-cloud-admin-compute/continuous_integration/se Vulnerability rules that target the build tool can allow specific vulnerabilities by creating an exception and setting the effect to 'ignore'. Block them by creating an exception and setting hte effect to 'fail'. For example, you could create a vulnerability rule that explicitly allows CVE-2018-1234 to suppress warnings in the scan results.
NEW QUESTION 54
The Prisma Cloud administrator has configured a new policy.
Which steps should be used to assign this policy to a compliance standard?
- A. Edit the policy, go to step 3 (Compliance Standards), click + at the bottom select the compliance standard, fill in the other boxes, and then click Confirm
- B. Custom policies cannot be added to existing standards.
- C. Open the Compliance Standards section of the policy, and then save.
- D. Create the Compliance Standard from Compliance tab. and then select Add to Policy.
Answer: A
NEW QUESTION 55
A customer wants to harden its environment from misconfiguration
Prisma Cloud Compute Compliance enforcement for hosts covers which three options? (Choose three.)
- A. Host cloud provider tags
- B. Hosts without Defender agents
- C. Docker daemon configuration files
- D. Host configuration
- E. Docker daemon configuration
Answer: B,C,D
NEW QUESTION 56
Match the service on the right that evaluates each exposure type on the left.
(Select your answer from the pull-down list. Answers may be used more than once or not at all.)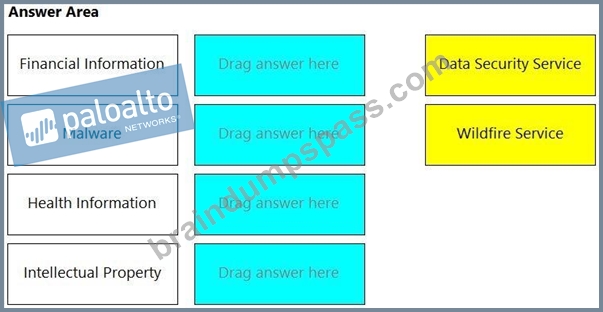
Answer:
Explanation: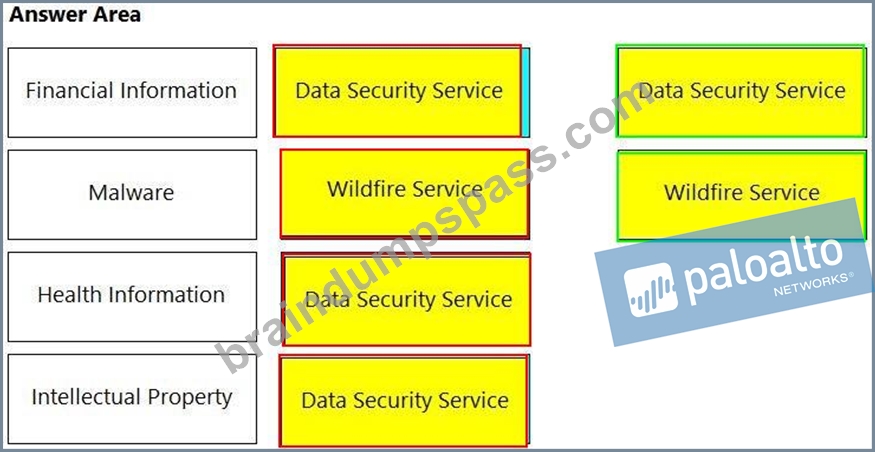
Reference:
https://www.paloaltonetworks.com/prisma/cloud/cloud-data-security
NEW QUESTION 57
Put the steps involved to configure and scan using the IntelliJ plugin in the correct order.
Answer:
Explanation: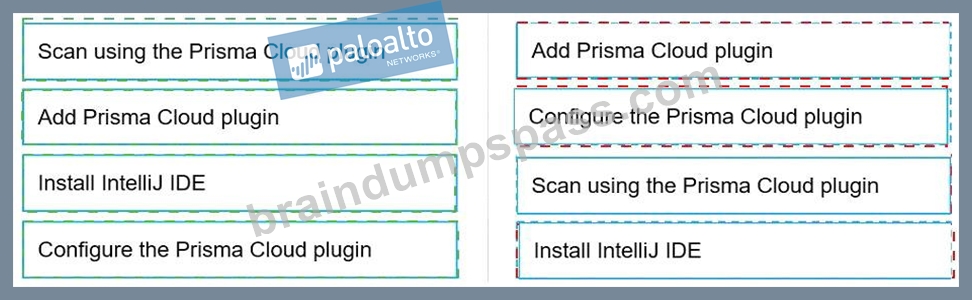
Explanation
Graphical user interface, text, application, chat or text message Description automatically generated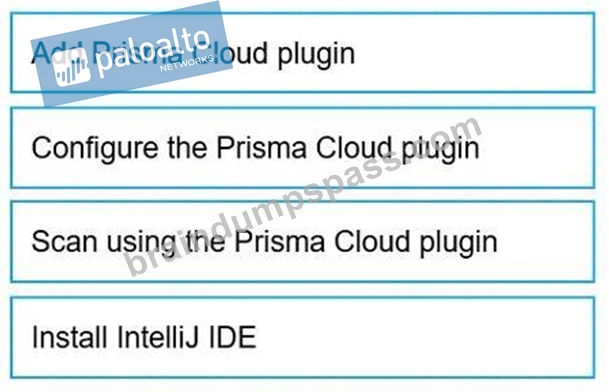
NEW QUESTION 58
Match the service on the right that evaluates each exposure type on the left.
(Select your answer from the pull-down list. Answers may be used more than once or not at all.)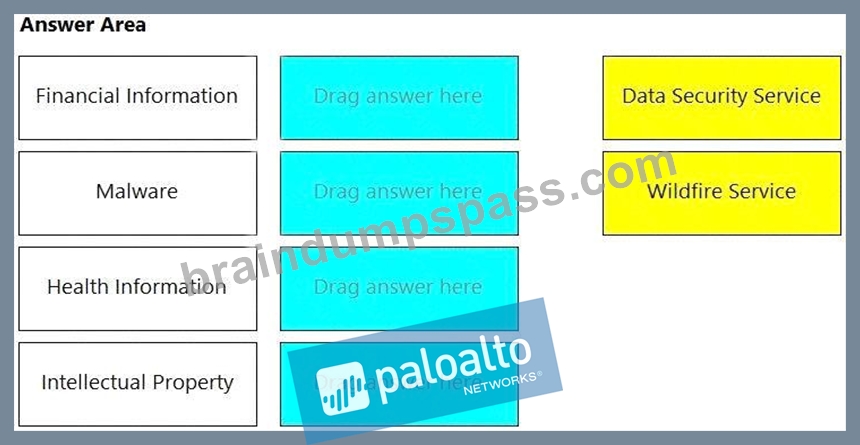
Answer:
Explanation: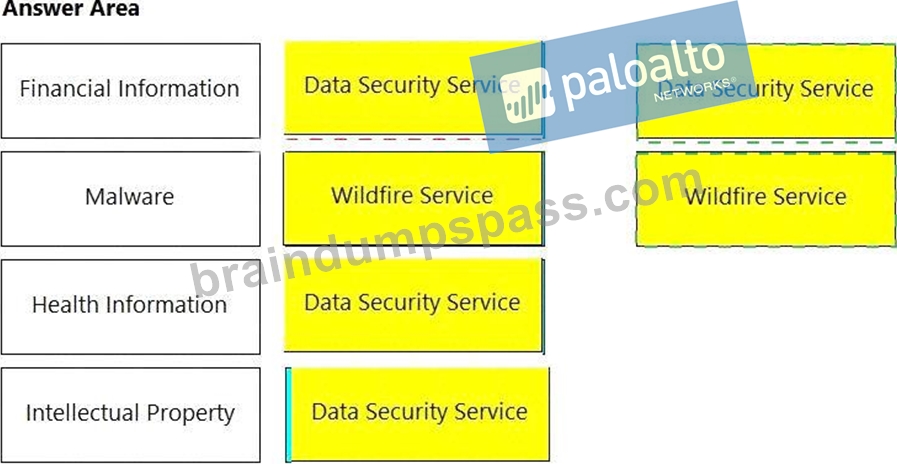
Explanation
Diagram Description automatically generated
NEW QUESTION 59
The development team wants to fail CI jobs where a specific CVE is contained within the image. How should the development team configure the pipeline or policy to produce this outcome?
- A. Set the specific CVE exception as an option in Jenkins or twistcli.
- B. Set the specific CVE exception as an option in Defender running the scan.
- C. Set the specific CVE exception as an option using the magic string in the Console.
- D. Set the specific CVE exception in Console's CI policy.
Answer: C
NEW QUESTION 60
Which statement is true about obtaining Console images for Prisma Cloud Compute Edition?
- A. To retrieve Prisma Cloud Console images using basic auth:
1. Access registry.paloaltonetworks.com, and authenticate using 'docker login'.
2. Retrieve the Prisma Cloud Console images using 'docker pull'. - B. To retrieve Prisma Cloud Console images using URL auth:
1. Access registry-url-auth.twistlock.com, and authenticate using the user certificate.
2. Retrieve the Prisma Cloud Console images using 'docker pull'. - C. To retrieve Prisma Cloud Console images using basic auth:
1. Access registry.twistlock.com, and authenticate using 'docker login'.
2. Retrieve the Prisma Cloud Console images using 'docker pull'. - D. To retrieve Prisma Cloud Console images using URL auth:
1. Access registry-auth.twistlock.com, and authenticate using the user certificate.
2. Retrieve the Prisma Cloud Console images using 'docker pull'.
Answer: C
Explanation:
Section: (none)
Explanation
NEW QUESTION 61
The development team wants to block Cross Site Scripting attacks from pods its environment How should the team construct the CNAF policy to protect against this attack?
- A. create a Container CNAF policy, targeted at a specific resource, check the box for XSS attack protection and set the action to prevent
- B. create a Container CNAF policy, targeted at a specific resource, check the box for XSS attack protection and set the action to alert
- C. create a Host CNAF policy targeted at a specific resource, check the box for XSS attack protection and set the action to "prevent"
- D. create a Container CNAF policy, targeted at a specific resource, and they should set "Explicitly allowed inbound IP sources" to the IP address of the pod.
Answer: C
NEW QUESTION 62
Which options show the steps required after upgrade of Console?
- A. Upgrade Defenders
Upgrade Jenkins Plugin
Upgrade twistcli where applicable - B. Uninstall Defenders
Upgrade Jenkins Plugin
Upgrade twistcli where applicable
Allow the Console to redeploy the Defender - C. Update the Console image in the Twistlock hosted registry
Update the Defender image in the Twistlock hosted registry
Uninstall Defenders - D. Update the Console image in the Twistlock hosted registry
Update the Defender image in the Twistlock hosted registry
Redeploy Console
Answer: B
NEW QUESTION 63
......
PCCSE Exam Questions – Valid PCCSE Dumps Pdf: https://www.braindumpspass.com/Palo-Alto-Networks/PCCSE-practice-exam-dumps.html
Verified PCCSE dumps Q&As - Pass Guarantee: https://drive.google.com/open?id=1rNzZC8qsIClKRHlkghZMGIXSft2xBLA1